VSP-8284XSQ:1(config)#show run mod ?
boot Display boot configuration
cfm Display cfm configuration
chef Display chef configuration
cli Display cli configuration
diag Display diag configuration
dvr Display dvr configuration
eap Display eap configuration
energy-saver Display energy-saver configuration
fa Display fa configuration
fhs Display fhs configuration
filter Display filter configuration
ike Display ike configuration
ip Display ip configuration
ipsec Display ipsec configuration
ipv6 Display ipv6 configuration
isis Display isis configuration
i-sid Display i-sid configuration
lacp Display lacp configuration
license Display license configuration
lldp Display lldp configuration
lst Display lst configuration
macsec Display macsec configuration
mlt Display mlt configuration
naap Display naap configuration
nls Display nls configuration
ntp Display ntp configuration
ovsdb Display ovsdb configuration
port Display port configuration
qos Display qos configuration
radius Display radius configuration
rmon Display rmon configuration
sflow Display sflow configuration
security Display security configuration
slamon Display slamon configuration
slpp Display slpp configuration
smtp Display smtp configuration
spbm Display spbm configuration
stg Display stg configuration
sys Display sys configuration
tacacs Display tacacs configuration
vlan Display vlan configuration
web Display web configuration
vxlan Display vxlan configuration
Author Archives: avayarob
Trace Level
core1:1#show trace modid-list
0 – COMMON 126 – MRP
1 – SNMP 127 – EFM
2 – RMON 128 – DHU
3 – PORT_MGR 129 – N/A
4 – CHAS_MGR 130 – N/A
5 – BRIDGE 131 – ERCD_DHCPS
6 – OSPF 132 – KHI
7 – HWIF 133 – NETWRS
8 – SIM 134 – NETINET
9 – CPP 135 – OS
10 – NETDRV 136 – VXNET
11 – VLAN_MGR 137 – USR
12 – CLI 138 – VXCONFIG
13 – MAIN 139 – OSAL
14 – P2IP 140 – MISC
15 – RCIP 141 – SHELL
16 – WEBSRV 142 – MESSAGE
17 – ACIF 143 – LCD
18 – GBIF 144 – COP
19 – 145 – ZLIB
20 – TDP 146 – SF
21 – MAN_DIAG 147 – MESSAGE
22 – MAN_TEST 148 – LCD
23 – IGMP 149 – COP
24 – IPFIL 150 – QOS
25 – MLT 151 – COP
26 – IPPOLICY 152 – IM
27 – IPMC 153 – IMG_SYNC
28 – SYSLOG 154 – LOG
29 – DVMRP 155 – CAN
30 – P2IPX 156 – LC
31 – RCIPX 157 – RESET
32 – RAPTARU 158 – CPP-AGENT
33 – OCTAPID 159 – HBELIB
34 – BOOT 160 – CORE
35 – IOM 161 – SHRLOG
36 – QOS 162 – WD_APP
37 – FLEXDB 163 – WD_PROC
38 – SMM 164 – CPP_COMMON
39 – ATM 165 – PatchManager
40 – POS 166 – RCIP_OSPF
41 – RADIUS 167 – RCIP_RIP
42 – SIO_COM 168 – RCIP_PIM
43 – PGM 169 – RCIP_IGMP
44 – ORNA 170 – RCIP_DHCP
45 – RTM 171 – RCIP_VRRP
46 – P2CMN 172 – RCIP_UDP
47 – RIP 173 – RCIP_RSMLT
48 – PIM 174 – RCIP_POLICY
49 – RPS 175 – VSP_TALK
50 – NTP 176 – CLILOG
51 – TCP 177 – SNMPLOG
52 – BGP 178 – L2VPN
53 – EPILOGUE 179 – ERCD_SPBM
54 – SSH 180 – LLDP
55 – AUTOMAT 181 –
56 – HAL 182 –
57 – WIND 183 – SPBPT
58 – EAP 184 – LMF
59 – LACP 185 – VPE_MAC
60 – PING 186 – HCK
61 – DNS 187 – VPE_VLAN
62 – DPM 188 – VPE_IPV4
63 – BOOTP 189 – VPE_ARP
64 – DPMMSG 190 – VPE_IPMC
65 – FILTER 191 – VPE_IPV6
66 – RCIP6 192 – SLAMON
67 – MESSAGE 193 – VPE_BRIDGE
68 – LCD 194 – VPE_MLT
69 – RCD 195 – VPE_PORT
70 – RLCD 196 – VPE_SPBM
71 – PD 197 – DBG
72 – COP 198 – PORT_L1
73 – ERCD 199 – POE
74 – ERCD_VLAN 200 – VPE_FILTER
75 – ERCD_PORT 201 – VPE_QOS
76 – ERCD_MLT 202 – VPE_IPFIX
77 – ERCD_MGID 203 – EVT
78 – ERCD_MAC 204 – VPE_FABRIC
79 – ERCD_HA 205 – VPE_DRIVER
80 – ERCD_IP 206 – VPE_TBLMGR
81 – ERCD_IPMC 207 – UNI
82 – ERCD_IPX 208 – VPE_CONCHK
83 – ERCD_IPV6 209 – VPE_UTL
84 – ERCD_IPFIX 210 – VPE_POLICER
85 – ERCD_FILTER 211 – MACSEC
86 – ERCD_QOS 212 – VPE_HEARTBEAT
87 – ERCD_MPLS 213 – VPE_CMD
88 – ERCD_IPVPN 214 – VPE_VL
89 – F2I 215 – VPE_COB
90 – F2E 216 – VPE_PATCH
91 – FOQ 217 – VPE_RSP
92 – HWIFCOP 218 – ASG
93 – IPFIX 219 – ASG_UTILS
94 – IPMC6 220 – VPE_MACSEC
95 – MCAST6_CMN 221 – FA
96 – MLD 222 – ONA
97 – PIM6 223 – PIMGW
98 – SLPP 224 – MOCANA
99 – INFINITY 225 – FHS
100 – MPLS 226 – ERCD_FHS
101 – RCMPLS 227 – VRRPV3
102 – ACLI 228 – DBSYNC
103 – VRF 229 – DVR
104 – NSNA 230 – SMTP
105 – MIRRORFPGA 231 – VXLAN
106 – MSTP 232 – SFLOW
107 – RSTP 233 – IKE
108 – MSDP 234 – DIGITALCERT
109 – TACACS 235 – OPENSSL
110 – BFD 236 – CHEF
111 – OPM 237 – CHEFCLIENT
112 – MSG_API 238 – IPSEC
113 – DISPATCHER 239 – SECURITY
114 – MAILBOX_DRV 240 – ERCD_SECURITY
115 – TLS 241 – SLPPG
116 – ADM 242 – NLS_BASE
117 – RBS 243 – NLS_SSIO
118 – TDCONT 244 – OVSDBIF
119 – ISIS 245 – VCS
120 – CFM 246 – VCS_CLIENT
121 – OERCD 247 – NICKNAME_SERVER
122 – PWE3 248 – NICKNAME_CLIENT
123 – EXTENDED_PING 249 – ENERGY_SAVER
124 – LOOPBACK 250 – MULTIPLE_USERS
125 – SPBM 251 – LST
252 – NLS_NFT
core1:1#trace level 9 ?
<0-4> Trace level (0-Disabled; 1-Very terse; 2-Terse; 3-Verbose; 4-Very verbose)
core1:1#clear trace
core1:1#trace level 9 2
core1:1#trace shut
core1:1#show trace file tail
core1:1#save trace
Save trace to file /intflash/systrace successful.
283 written to /intflash/systrace
Run SPBM
VSP-8284XSQ:1(config)#run ?
Run commands
spbm Run SPBM commands
VSP-8284XSQ:1(config)#run spbm
**********************************************************
*** This script will guide you through configuring the ***
*** Extreme Networks switch for optimal operation of SPB. ***
*** —————————————————***
*** The values in [] are the default values, you can ***
*** input alternative values at any of the prompts. ***
*** If you wish to terminate or exit this script ***
*** enter ^C <control-C> at any prompt. ***
*** NOTE: THE COMMAND WILL TEMPORARILY FLAP IS-IS,SPBM ***
**********************************************************
SPB Ethertype <0x8100,0x88a8> [0x8100]:
SPBM instance <1-100> [1]:
SPB primary BVLAN <2-4059> [4051]:
SPB secondary BVLAN <2-4059> [4052]:
ISIS system id <xxxx.xxxx.xxxx> [0051.0064.c884]:
SPB nickname <x.xx.xx> [4.c8.84]:
SPB Manual Area <xx.xxxx.xxxx…xxxx> [49.0000]:
ISIS System Name [VSP-8284XSQ]:
Enable SPBM multicast (y/n) [n]:
Enable IP shortcuts (y/n) [n]:
Configure SPBM SMLT? (y/n) [n]:
ISIS port interfaces <a/b,c/d>[]:
ISIS MLT interface <MLT ID LIST> []:
Enable CFM SPBM (y/n) [n]:
****CONFIGURATION IN PROGRESS****
VSP-8284XSQ:1(config)#no router isis enable
VSP-8284XSQ:1(config)#router isis
VSP-8284XSQ:1(config-isis)#no ip-source-address
VSP-8284XSQ:1(config-isis)#no system-id
VSP-8284XSQ:1(config-isis)#configure terminal
Enter configuration commands, one per line. End with CNTL/Z.
VSP-8284XSQ:1(config)#spbm
VSP-8284XSQ:1(config)#spbm ethertype 0x8100
VSP-8284XSQ:1(config)#router isis
VSP-8284XSQ:1(config-isis)#spbm 1
VSP-8284XSQ:1(config-isis)#spbm 1 nick-name 4.c8.84
VSP-8284XSQ:1(config-isis)#spbm 1 b-vid 4051,4052 primary 4051
VSP-8284XSQ:1(config-isis)#vlan create 4051 type spbm-bvlan
VSP-8284XSQ:1(config)#vlan create 4052 type spbm-bvlan
VSP-8284XSQ:1(config)#router isis
VSP-8284XSQ:1(config-isis)#system-id 0051.0064.c884
Error: Attribute field already configured to the same value.
VSP-8284XSQ:1(config-isis)#manual-area 49.0000
VSP-8284XSQ:1(config-isis)#sys-name VSP-8284XSQ
VSP-8284XSQ:1(config-isis)#router isis enable
VSP-8284XSQ:1(config)#
****SCRIPT EXECUTION COMPLETE****
VSP-8284XSQ:1(config)#1 2018-05-16T11:03:24.585Z VSP-8284XSQ CP1 – 0x00000003 – 00000000 GlobalRouter SW INFO Dynamic nick-name client has been started
1 2018-05-16T11:03:24.707Z VSP-8284XSQ CP1 – 0x00000004 – 00000000 GlobalRouter SW INFO Dynamic nick-name client has been stopped
VSP-8284XSQ:1(config)#
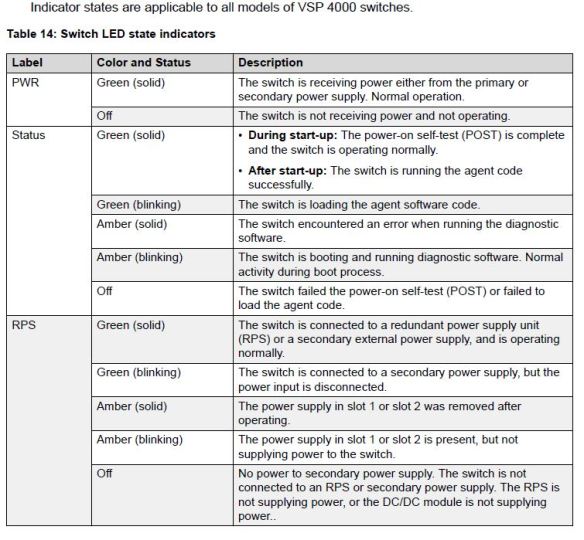
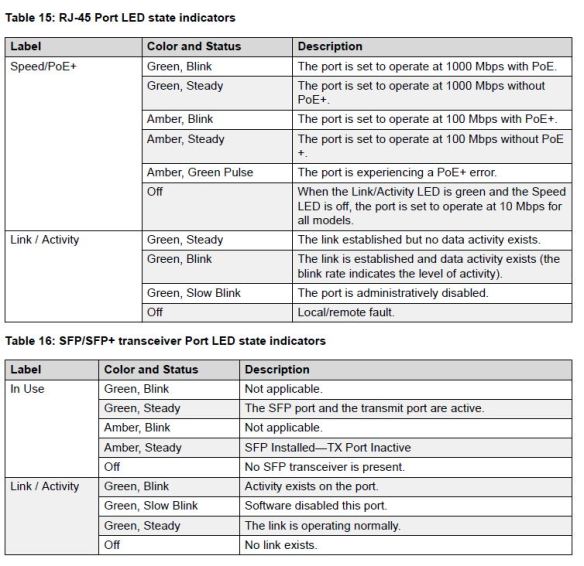
VSP 4000 LED Status


Troubleshooting
Windows:
ping -v is now deprecated which was useful for sending ICMP with TOS field values. Try ping -Q as alternative from a UNIX machine.
Unix:
ping –Q
-Q tos Set Quality of Service -related bits in ICMP datagrams. tos can be
either decimal or hex number. Traditionally (RFC1349), these have
been interpreted as: 0 for reserved (currently being redefined as
congestion control), 1-4 for Type of Service and 5-7 for Prece-
dence. Possible settings for Type of Service are: minimal cost:
0x02, reliability: 0x04, throughput: 0x08, low delay: 0x10. Multi-
ple TOS bits should not be set simultaneously. Possible settings
for special Precedence range from priority (0x20) to net control
(0xe0). You must be root (CAP_NET_ADMIN capability) to use Criti-
cal or higher precedence value. You cannot set bit 0x01 (reserved)
unless ECN has been enabled in the kernel. In RFC2474, these
fields has been redefined as 8-bit Differentiated Services (DS),
consisting of: bits 0-1 of separate data (ECN will be used, here),
and bits 2-7 of Differentiated Services Codepoint (DSCP).
Man curl or curl –help
Curl can be useful to check TCP connections for http or https.
Result could be Connection Timeout, Connection Refused or Connected (200 OK).
VOSS Features
VOSS 7.0
Max number IP interfaces: 506
(Result upon adding IP interface 507 – Error: Insufficient resources available to create IP.)
Max number DHCP-Relay Fwd-Path: 1024
Max number DHCP-Relay Fwd-Path per VLAN: 10
(Result upon adding 11th Fwd-Path – Error: DHCP maximum number of forwarding records added)
VOSS interfaces are shutdown by default so have to do no shutdown command within interface context.
Assigning IP to many VLANs with IP and DHCP-Relay
Assumption: VLANs created 1024-2048
Python script to generate config script file (pass1vlanip.py)…
vl_fr = 1024
vl_to = 1278
pass1oct3 = 0
dhcpsrv = “10.10.10.10”
mask = “255.255.255.0”
for value in range (vl_fr,vl_to):
pass1oct3 = pass1oct3 + 1
ipadd = “1.1.” + str (pass1oct3) + “.1”
with open(‘pass1vlanip.cfg’, ‘a’) as outfile:
outfile.write(“\ninterface vlan ” + str (value))
outfile.write(“\nip address ” + str (ipadd) + ” ” + str (mask))
outfile.write(“\nip dhcp-relay”)
outfile.write(“\nexit”)
outfile.write(“\nip dhcp-relay fwd-path ” + str (ipadd) + ” ” + str (dhcpsrv))
outfile.write(“\nip dhcp-relay fwd-path ” + str (ipadd) + ” ” + str (dhcpsrv) + ” enable”)
outfile.write(“\nip dhcp-relay fwd-path ” + str (ipadd) + ” ” + str (dhcpsrv) + ” mode bootp_dhcp”)
Note: Create multiple files for each “pass” with different value in second octet to create batches of class C subnets 254 hosts (pass1vlanip.py, pass2vlanip.py, etc…).
Part of the output file (ie pass1vlanip.cfg):
interface vlan 1024
ip address 1.1.1.1 255.255.255.0
ip dhcp-relay
exit
ip dhcp-relay fwd-path 1.1.1.1 10.10.10.10
ip dhcp-relay fwd-path 1.1.1.1 10.10.10.10 enable
ip dhcp-relay fwd-path 1.1.1.1 10.10.10.10 mode bootp_dhcp
interface vlan 1025
ip address 1.1.2.1 255.255.255.0
ip dhcp-relay
exit
ip dhcp-relay fwd-path 1.1.2.1 10.10.10.10
ip dhcp-relay fwd-path 1.1.2.1 10.10.10.10 enable
ip dhcp-relay fwd-path 1.1.2.1 10.10.10.10 mode bootp_dhcp
interface vlan 1026
ip address 1.1.3.1 255.255.255.0
ip dhcp-relay
exit
ip dhcp-relay fwd-path 1.1.3.1 10.10.10.10
ip dhcp-relay fwd-path 1.1.3.1 10.10.10.10 enable
ip dhcp-relay fwd-path 1.1.3.1 10.10.10.10 mode bootp_dhcp
Rename .cfg file as .run file and move to .acli folder so that ACLI terminal can source the files.
From ACLI login to switch and type @run pass1ip.run which will run the commands created by the python script. This speeds up the process of creating multiple configuration entries such as VLANs, IP addresses, DHCP etc…
Another example script to delete a range of VLANs (delvlan.py):
vl_fr = 1024
vl_to = 2048
for value in range (vl_fr,vl_to):
with open(‘delvlan.cfg’, ‘a’) as outfile:
outfile.write(“\nvlan delete ” + str (value))
value = value + 1
with open(‘delvlan.cfg’, ‘a’) as outfile:
outfile.write(“\nvlan delete ” + str (value))
Output file (delvlan.cfg):
vlan delete 1024
vlan delete 1025
vlan delete 1026
vlan delete 1027
vlan delete 1028
etc…
Rename delvlan.run and type @run delvlan.run in ACLI terminal will remove long list of VLANs and all underlying VLAN configuration such as the IP address and VRRP. Otherwise have to delete each VLAN individually as there is no range parameter.
Shortest Path Bridging
https://www.youtube.com/channel/UCn8AhOZU3ZFQI-YWwUUWSJQ
802.1aq Wikipedia site – http://en.wikipedia.org/wiki/802.1aq
EMC Alarms and Events
Add User to EMC
From the OS add a new user. In VMWare login as root into the console and use the useradd <name> command to create the new user. Set a password with the passwd <name> command. You also need to add the user in EMC under Administration>Users and specify the group access.
Aside… to search for config files archived by EMC in the virtual appliance type…
find / -name *.cfg
Inventory Manager>Data Storage>Directory Path
Specify the base directory where data for Inventory Manager is stored. This data includes capacity reports, configuration templates, configurations, and property files.
/usr/local/Extreme_Networks/NetSight/appdata/InventoryMgr
ls -alg to see file attributes.
https://www.ibm.com/support/knowledgecenter/en/SSLTBW_2.3.0/com.ibm.zos.v2r3.bpxa500/lscmd.htm
Changing file attributes…
chmod -R 775 or 777 .
N Description ls binary
0 No permissions at all --- 000
1 Only execute --x 001
2 Only write -w- 010
3 Write and execute -wx 011
4 Only read r-- 100
5 Read and execute r-x 101
6 Read and write rw- 110
7 Read, write, and execute rwx 111
- First Number 7 – Read, write, and execute for user.
- Second Number 5 – Read and execute for group.
- Third Number 5 – Read and execute for other.
Which group user belongs…
id -Gn [user] or groups or id user